From 88 Suppliers in Two Years to Over a Million Cyber Risk Assessments a Day
Cyber Tzar has reached a major engineering milestone: more than one million triage-level organisational assessments a day, bringing population-scale cyber risk intelligence within reach and laying the foundations for the Universal Cyber Risk Score.
Traditional third-party cyber risk assessment is slow, expensive and difficult to scale. Gathering supplier documentation, reviewing penetration-test reports, interpreting vulnerabilities and negotiating risk decisions can take weeks or months per organisation. For businesses with thousands of suppliers, assessing everyone has historically been impractical.
Cyber Tzar is changing that.
Following an intensive 96-hour engineering sprint, our new triage capability supports more than one million organisational assessments a day, drawing on five years of accumulated cyber risk evidence covering more than 7.4 million organisations.
Triage That Goes Beyond a Cyber Rating
Cyber Tzar Triage is not a superficial website check. It rapidly discovers infrastructure, application technologies, software, and observable software versions, along with organisational and supplier dependencies, delivering actionable cyber risk intelligence at population scale.
Consider PHP2Shell (CVE-2026-109618 and CVE-2026-109619), two critical PHP vulnerabilities disclosed in October 2026. By identifying PHP deployments and observable versions, Cyber Tzar can rapidly highlight organisations potentially affected by these vulnerabilities, helping security teams prioritise investigation and remediation across thousands of organisations. Correlating those findings with contemporary threat intelligence provides further context. Version identification indicates potential exposure; confirming a vulnerability also requires considering patch status and deployment conditions.
Triage also identifies third-party suppliers, assesses upstream exposure, and flags concentration risk by revealing where apparently independent organisations rely on the same underlying technology, provider, or infrastructure. This means we can investigate not only which organisations may be exposed to a vulnerability such as PHP2Shell, but also how that exposure could affect interconnected supply chains.
For customers requiring greater depth, Cyber Tzar provides comprehensive non-intrusive assessments of infrastructure, ports, services, software and vulnerabilities, followed by authorised intrusive testing where appropriate.
Evidence, Threat Intelligence and Context
At the heart of Cyber Tzar is our Virtuous Triangle: vulnerability assessment, contemporary threat intelligence and contextual risk assessment.
Rather than applying arbitrary checklist weights or inventing missing information, Cyber Tzar correlates observed technical exposure with relevant threats to produce consistent, evidence-driven assessments.
We do not fictionalise risk.
The objective is not simply to assign organisations a number. It helps security teams identify what matters, prioritise remediation, and understand how risk propagates through suppliers and shared infrastructure.
Assess Everybody. Then Start Fixing Things.
Consider an organisation with 10,000 suppliers.
Cyber Tzar can generate prioritised triage intelligence across that population in less than a day, including upstream dependencies and concentration risk. Customer-ready reporting may take two or three days, while comprehensive non-intrusive assessments across the same population take approximately a week. These are indicative operational timings.
The result is a fundamental shift in the economics of third-party risk management.
Instead of spending months deciding which suppliers to assess, organisations can start with a population-wide view and focus their resources on three practical decisions: accept the risk, help the supplier improve, or find an alternative and offboard.
Supplier improvement matters to us. Cyber Tzar is designed to help suppliers engage with the evidence, address weaknesses and demonstrate progress: not simply receive a rating.
Democratising Cyber Risk Intelligence
We believe in democratising data, functionality and capability. For too long, sophisticated cyber risk intelligence has been the preserve of large enterprises with the budgets, specialist teams and infrastructure to obtain it.
Cyber Tzar is changing that. By making enterprise-class assessment capabilities available at unprecedented scale, we can put meaningful cyber risk intelligence within reach of organisations of every size, their suppliers and, ultimately, individuals.
The Universal Cyber Risk Score takes that ambition further: making a consistent, evidence-driven measure of cyber risk publicly accessible, while Cyber Tzar provides the deeper intelligence and capabilities needed to understand and address it.
Enterprise-class intelligence should not require an enterprise-class budget.
Introducing the Universal Cyber Risk Score
This engineering milestone also brings us closer to launching the Universal Cyber Risk Score (UCRS).
The UCRS will provide a public-facing cyber risk score from 0 to 1,000, where higher is better, alongside a comparative index showing how organisations rank against others across industries and countries.
The public score will make cyber risk easier to understand and compare. Cyber Tzar will continue to provide the deeper proprietary intelligence, supplier analysis, assessment capabilities and remediation insights behind it.
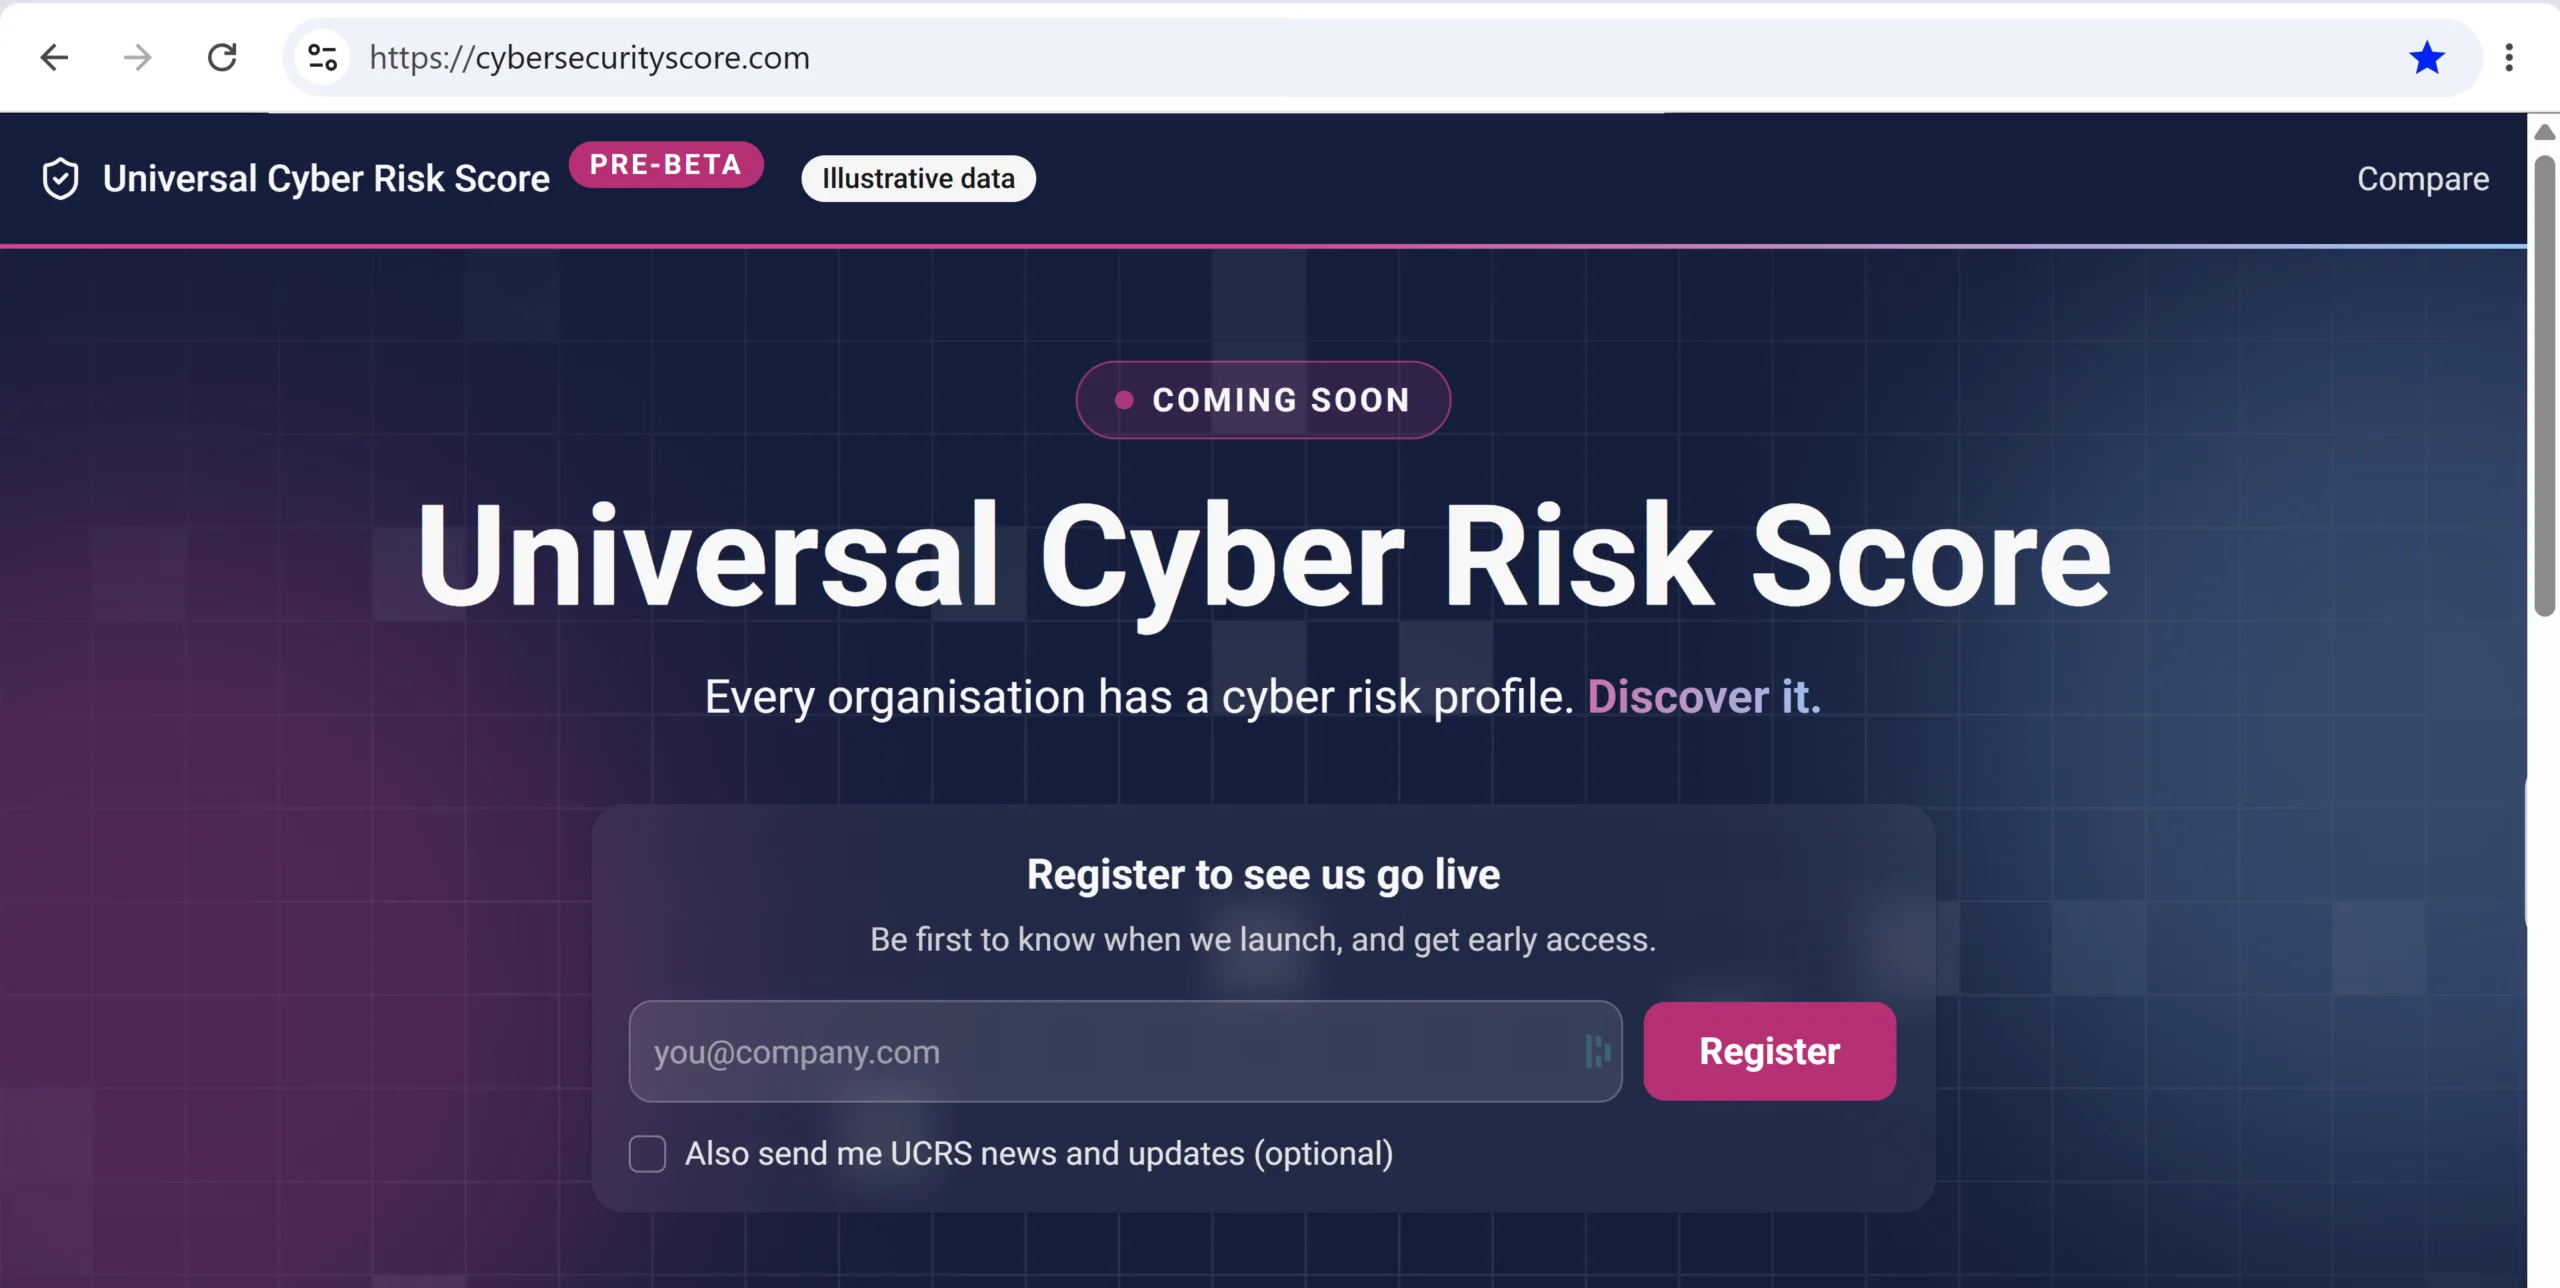
The Universal Cyber Risk Score is currently in pre-beta. The website includes illustrative preview data, and the public scoring service has not launched yet.
Explore the preview and register for early access at CyberSecurityScore.com.
For the full story behind the breakthrough, read Wayne Horkan’s 25-year journey from assessing 88 suppliers in two years to more than a million assessments a day.
Cyber Tzar: Quantify. Prioritise. Resilient.